XSolutions IT
  • About ▾
    • About Us
    • Our Process
    • Our Reviews
    • Refer and Earn
  • Solutions ▾
    • Complete Managed IT
    • Co-Managed IT
    • Managed Cybersecurity
    • Backup & Disaster Recovery
    • Cloud Data Protection
  • Industries ▾
    • Law Firms
    • Construction + Trades
    • Distribution + Supply Chain
    • Nonprofits
  • Service Areas▾
    • Rockland County NY
    • Westchester County NY
    • Bergen County NJ
  • Resources ▾
    • Free Resources for Law Firms
    • Free Resources for Construction
    • Free Resources for Distributors
    • Free Resources for Nonprofits
    • Newsletters
    • Blogs
  • Contact
  • 877-807-1332
  • Menu Menu
Looking Into Privacy Data

State Privacy Laws Coming. Are You Ready?

November 5, 2019/in Blog/by Joe Imperato, Sr.

Introduction

After the General Data Protection Regulation (GDPR) went into full effect in May 2019, many states in the U.S., seeing the Federal Government lagging in this area, have taken up the fight and either enacted or are in the process of creating regulations covering privacy, data security, cybersecurity, and data breach notification.

Larger corporations have robust legal departments advising them on changing regulations and compliance. Most Small-to-Medium Size Businesses (SMBs) do not.

Think about this scenario: One of your employees notifies you that they lost their laptop over the weekend. Aside from the cost and inconvenience of buying a new laptop, could you be on the hook for higher costs, and should you notify all your clients? Maybe, depending on where you live, the type of data stored, and whether the hard drive was encrypted.

A recent CSO Online post detailed 11 states that either enacted privacy regulations or will shortly.  The point is, GDPR let the genie out of the bottle, and many more states will follow suit. Are you ready?

Data of all kinds have grown exponentially

Companies are storing more and more data, and most states are starting to aggressively enforce data breach and security laws, setting out the responsibilities for businesses capturing and storing personal data.

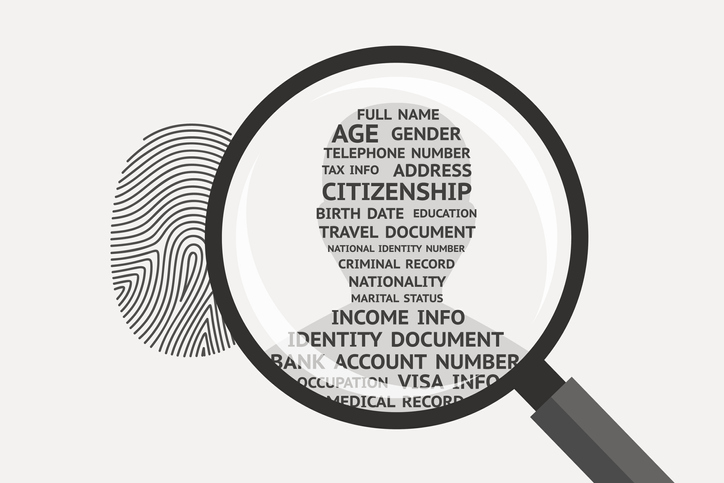
What do most states consider confidential or sensitive data? Medical and financial records such as credit card numbers, credit scores, and bank account numbers, but also addresses and phone numbers, social security numbers, birthdays, and in some cases purchase history—information that almost every single company normally keeps on their clients.

Many companies aren’t even sure exactly what kinds of data they’re capturing and storing!

With millions of cyber-criminals working around-the-clock to hack systems, and with employees accessing more and more confidential data daily, there is no known way to absolutely, positively guarantee you won’t have a data breach. However, your efforts to put in place good, solid best practices in security will go a long way to help you comply with current law and hopefully avoid hefty fines.

Start with the basics

  • Manage access to information. Who can access the confidential information you store in your business? Is this information easily accessible by everyone in your company? What is your policy about taking data out of the office on mobile devices?
  • Get serious about IT security and passwords. The more sensitive the data, the higher the level of security you need to keep on it. Are your passwords easy to crack? Is the data encrypted? Are they secured behind a strong firewall? If not, why not?
  • Train your employees. One of the biggest causes of data breaches are employees who accidentally download viruses and malware, allowing hackers to gain entry and steal your data. Do you have a data security policy? A password policy? Do you have training programs to help employees understand how to protect themselves and your company when using e-mail and the Internet?
  • Make sure you can restore data quickly. The GDPR’s Article 32 1 (c) titled “Security of processing” covers expectations relating to data security.  It states, in part, that responsible entities must have: “the ability to restore the availability and access to personal data in a timely manner in the event of a physical or technical incident.”  Some State regs have similar provisions.

    A managed Hybrid-cloud Business Continuity solution can reduce downtime to just minutes and hours versus days and weeks using data only backup systems. Get expert advice.
  • Physical security. Thieves can break into offices and steal servers, laptops, and other digital devices,  and paper documents. Are hard drives on all mobile devices encrypted? Are physical documents locked every night, and those containing personal data shredded when no longer needed? Are servers located in a locked room with restricted access?

Operating in multiple states is tricky

You are subject to the data privacy laws of the states in which you do business. Review the regulations of each state and create a data security plan that encompasses them all. A daunting task!

My suggestion is to use the GDPR as a basis of your security plan. It is the most comprehensive and wide-reaching of all privacy regulations worldwide, so far. If you use it as your model, you’ll know what kind of data you have, where it is installed, what protections you presently have, and a plan to come into full compliance.

Conclusion

EVERY business is responsible for data security. Not addressing this important issue has consequences that go beyond the legal aspect; it can seriously harm your reputation with clients. So be smart about this. Read the GDPR and the privacy regulations of the states you operate in, and talk to an attorney that is knowledgeable about privacy laws.

Take action now; don’t put this important issue on the back burner.

 XSolutions is an Elite Partner of Datto, the world leader in Hybrid-Cloud Business Continuity solutions whose systems protect 460+ Petabytes of data with over 1400+ employees and 9 offices around the globe. Call (845) 362-9675 and let us introduce you to the ultimate defense against data loss—whatever the cause. Backup & Disaster Recovery | Business Continuity | Data Risk Assessment

Tags: confidential information, Data Security, GDPR, General data Protection Regulation, Privacy Laws
Share this entry
  • Share on Facebook
  • Share on X
  • Share on Pinterest
  • Share on LinkedIn
  • Share on Reddit
  • Share by Mail
https://xsolutions.com/wp-content/uploads/2019/11/Personal-Data-small.jpg 483 724 Joe Imperato, Sr. https://xsolutions.com/wp-content/uploads/2023/09/XSol-Logo-header-300x138.png Joe Imperato, Sr.2019-11-05 07:00:502026-10-13 12:11:58State Privacy Laws Coming. Are You Ready?
You might also like
Coming To America—Data Privacy Regulations!
GDPR GDPR and Business Continuity―why you must care
GDPR The Reach Is Long And The Bite Deep
Cyber Safe 7 Disaster Planning Essentials Your Business Should Act On Now
Free Checklist

Cybersecurity Checklist

Use this simple checklist to spot common cybersecurity gaps, strengthen your defenses, and start better conversations about protecting your business.

Recent Posts

  • 10 Hidden Technology Problems Costing Your Law Firm Billable Hours
  • Secure File Sharing for Law Firms | Managed IT Support
  • Managed IT Services & Cybersecurity for Law Firms in Rockland County, NY
  • 10 Keyboard Shortcuts Everyone Should Know
  • Why Summer Is a Risky Season for Business Cybersecurity
XSolutions Trademarked LOGO

XSolutions is a managed IT services and cybersecurity company based in New City, NY. Since 1999, we have helped businesses across Rockland County, Bergen County, Westchester County, Orange County, Northern New Jersey, and the greater NY/NJ/CT region reduce risk, improve reliability, and gain clarity over their technology. We specialize in proactive managed IT, cybersecurity, Microsoft 365, cloud, backup and disaster recovery, and strategic IT guidance for organizations with 15 or more computers.

Service Areas

    • Managed IT Nanuet, NY

    • Managed IT New City, NY

    • Managed IT Suffern, NY

    • Managed IT Rockland County

    • Managed IT Orange County

    • Managed IT Westchester County

    • Managed IT Putnam County

    • Managed IT Mahwah, NJ

    • Managed IT Ramsey, NJ

    • Managed IT Bergen County

    • Managed IT Essex County

    • Managed IT Passaic County

    • Managed IT Hudson County

Contact Us

20 Squadron Blvd., STE 320
New City, NY 10956
Sales: 877-807-1332
Support: 845-362-9675

Facebook  LinkedIn Twitter (X) YouTube


XSolutions® Consulting Services, LLC All rights reserved © 2026 | Privacy Policy | Sitemap
Link to: Security Alert: Phone Bank Scam Bilking Customers Link to: Security Alert: Phone Bank Scam Bilking Customers Security Alert: Phone Bank Scam Bilking CustomersHooded Hacker On Phone Scam Link to: Security Alert: Fake WebEx Invites Deliver Malware Instead Link to: Security Alert: Fake WebEx Invites Deliver Malware Instead Email PhishingSecurity Alert: Fake WebEx Invites Deliver Malware Instead
Scroll to top Scroll to top Scroll to top
XSolutions IT
This website uses cookies
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}