XSolutions IT
  • About ▾
    • About Us
    • Our Process
    • Our Reviews
    • Refer and Earn
  • Solutions ▾
    • Complete Managed IT
    • Co-Managed IT
    • Managed Cybersecurity
    • Backup & Disaster Recovery
    • Cloud Data Protection
  • Industries ▾
    • Law Firms
    • Construction + Trades
    • Distribution + Supply Chain
    • Nonprofits
  • Service Areas▾
    • Rockland County NY
    • Westchester County NY
    • Bergen County NJ
  • Resources ▾
    • Free Resources for Law Firms
    • Free Resources for Construction
    • Free Resources for Distributors
    • Free Resources for Nonprofits
    • Newsletters
    • Blogs
  • Contact
  • 877-807-1332
  • Menu Menu
Employee on cell phone

Anatomy Of A CEO-Wire Fraud Attack

June 6, 2017/in Article/by Joe Imperato, Sr.

CEO-Wire Fraud is a dangerous Social Engineering attack that cost businesses billions in losses. A good Social Engineer will study potential victims sometimes for months before attacking and craft convincing spoofed emails, targeting accounting personnel with wire transfer responsibilities.

Recently, one of our best clients experienced such an attack and they graciously allowed us to use the   email stream as an educational tool. This attack ultimately failed, but schemes like this succeed every day, so it is important that you train your staff accordingly. I’m not including all of the emails since there were over 15 of them, but I’ll show you enough so you’ll get the idea of how this type of attack unfolds.

Note: I redacted identifying information in the emails to protect our client’s privacy.

Email #1:
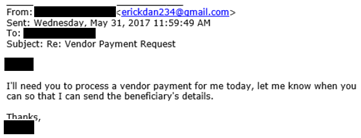
Comment: The attacker contacts his target masquerading as the boss. Hackers do their homework, often stalking companies on the internet (i.e. Google, social media, specialized commercial databases and using social engineering tactics) for weeks and even months to find people within a company with the right responsibilities to target.

Here’s a crucial piece of evidence: The “From” address had the boss’s name but the email of the sender was not from a company email address and in act didn’t even contain the boss’s name. Instead it was a Gmail account—a dead giveaway. Most people do not realize this and only look at the boss’s name before acting.

Email #2:
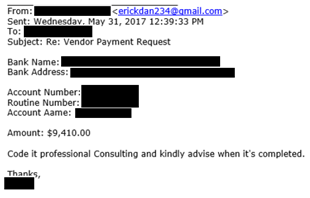
Email 2 - detailed instructions

Comment: The attacker sends the target detailed instructions for the wire transfer. Notice that the amount is below $10,000. This is probably due to the attacker’s belief that a small amount would not arouse suspicion, be considered routine and not trigger additional approvals.

Email #3:
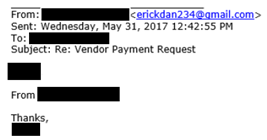
Email 3 - identified bank

Comment: Here’s a key point. This attacker knew that the targeted company had an account at a particular bank (which we redacted). As mentioned, scammers do their homework. Naming a bank or some other “insider information” is intended to give their targets confidence that the person sending the email is indeed the boss.

Email #4:
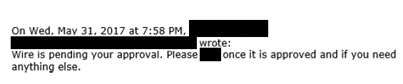
Email 4 - approval required

Comment: A glitch! Company procedures require the boss’s direct approval to wire funds. When the employee informs the attacker, the scammer comes up with a story.

Email #5:
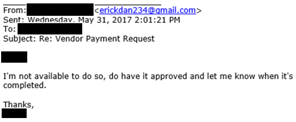
Email 5 - scammer lies

Comment: The attacker tries to salvage the scheme by explaining that he cannot approve it and tries to rely on his position as the “boss” to intimidate the employee into acting without the required approval.

Email #6:
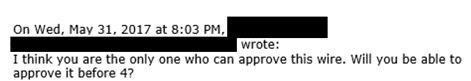
Email 6 - only CEO can approve

Comment: Things aren’t going so well at this point. Company procedures call for the boss’s direct approval, which the scammer cannot do without risking detection.

Email #7:
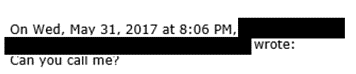
Email 7 - Employee asks to speak to boss

Comment: Suspicious, the employee now asks to talk to the boss directly. The attacker knows that once this happens, the ruse is over.  So, he makes up another excuse.

Email #8:
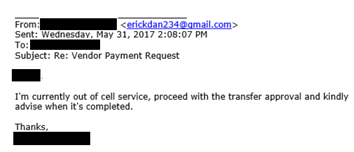
Email 8 - Attacker Lies Again

Comment: The attacker gives what seems like a reasonable explanation of why he cannot speak directly with his employee and again tries to manipulate the target into finding a way to wire the funds.

Email #9:
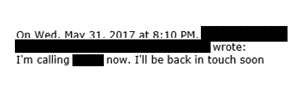
Email 9 - Employee verifies With Bank

Comment: The employee calls the bank (redacted) directly and then calls the boss, who verifies that he never made the wire request. The attack fails.

Key points:

  • Social Engineers are one of the most feared type of attackers. They know human nature and how to tap into emotions to get a desired response. A Social Engineer with good programming skills is an absolute nightmare to businesses and law enforcement.
  • When committing CEO-Wire Fraud, scammers go to great lengths to research their prey. The more they know about their target, the better they can pass themselves off as an “insider”.
  • To guard against a CEO-Wire Fraud attack, procedures should be in place to positively identify those with authority to approve such transactions.
  • Employees must be trained on the type of information they can divulge to the public versus specific information they should never divulge to anyone. One of the skills of a good Social Engineer is the ability to put together a detailed profile of a target company using various bits of seemingly unimportant information gleamed through the internet and telephone conversations.
  • Employees should be trained on how to spot bogus emails. In the instance above, why would the boss be using a non-company email account?
  • Home computers used to log into the corporate network should be secured. Hackers may send phish emails to employees’ home PCs knowing that many are not patched, are running outdated/vulnerable software and using less effective free anti-virus (AV) products or having no AV at all. Once infected, scammers can penetrate corporate networks when the employee logs in from home.
  • Employees should be encouraged to question suspicious instructions especially when asked to bypass procedures no matter who is making the request and to immediately notify their supervisor. Social Engineers use human nature against their targets and the fact that most are uncomfortable questioning authority.

Sound operational procedures, employee training, the willingness to question instructions when things don’t seem right without fear of retribution, a managed and maintained corporate network and a comprehensive Backup/Disaster Recovery solution will go a long way to keeping your business safe.

Don’t be a victim. Review your company’s operational procedures as they relate to wiring funds, setting up vendors in the accounting system and appropriate approval levels. The sad fact is that many times this type of fraud succeeds resulting in large financial losses. Be proactive and take the proper steps now.

XSolutions is an Elite Partner of Datto, the world leader in Hybrid-Cloud Business Continuity solutions whose systems protect 250+ Petabytes of data with over 800 employees around the globe. Call (845) 362-9675 and let us introduce you to the ultimate defense against data loss—whatever the cause.
Tags: Anti-Virus, Antivirus, AV, backup & disaster recovery, Business Continuity, CEO-wire Fraud, hacker, online scams, phishing, Security, spammer
Share this entry
  • Share on Facebook
  • Share on X
  • Share on Pinterest
  • Share on LinkedIn
  • Share on Reddit
  • Share by Mail
https://xsolutions.com/wp-content/uploads/2018/10/coffee-phone-man.jpg 266 702 Joe Imperato, Sr. https://xsolutions.com/wp-content/uploads/2023/09/XSol-Logo-header-300x138.png Joe Imperato, Sr.2017-06-06 09:30:392026-10-13 12:43:14Anatomy Of A CEO-Wire Fraud Attack
You might also like
Fake call center worker Call Center Exploits – What You Need To Know
Business Owners are at the end of their rope 5 Dangerous Beliefs That Can Destroy Your Business
security-network Security Alert: DocuSign Breach Leads To Phishing Attacks
Startled woman at PC COVID-19 Exposes Flaw In DR Plans
Challenges 12 Steps To Survive In The New Normal
sky You Waste 17 Hours Per Year On This
clipboard-server 5 Staggering Facts You Should Know
Server unit and computer cloud storage Business Backups: The Rule Of 3
Free Checklist

Cybersecurity Checklist

Use this simple checklist to spot common cybersecurity gaps, strengthen your defenses, and start better conversations about protecting your business.

Recent Posts

  • 10 Hidden Technology Problems Costing Your Law Firm Billable Hours
  • Secure File Sharing for Law Firms | Managed IT Support
  • Managed IT Services & Cybersecurity for Law Firms in Rockland County, NY
  • 10 Keyboard Shortcuts Everyone Should Know
  • Why Summer Is a Risky Season for Business Cybersecurity
XSolutions Trademarked LOGO

XSolutions is a managed IT services and cybersecurity company based in New City, NY. Since 1999, we have helped businesses across Rockland County, Bergen County, Westchester County, Orange County, Northern New Jersey, and the greater NY/NJ/CT region reduce risk, improve reliability, and gain clarity over their technology. We specialize in proactive managed IT, cybersecurity, Microsoft 365, cloud, backup and disaster recovery, and strategic IT guidance for organizations with 15 or more computers.

Service Areas

    • Managed IT Nanuet, NY

    • Managed IT New City, NY

    • Managed IT Suffern, NY

    • Managed IT Rockland County

    • Managed IT Orange County

    • Managed IT Westchester County

    • Managed IT Putnam County

    • Managed IT Mahwah, NJ

    • Managed IT Ramsey, NJ

    • Managed IT Bergen County

    • Managed IT Essex County

    • Managed IT Passaic County

    • Managed IT Hudson County

Contact Us

20 Squadron Blvd., STE 320
New City, NY 10956
Sales: 877-807-1332
Support: 845-362-9675

Facebook  LinkedIn Twitter (X) YouTube


XSolutions® Consulting Services, LLC All rights reserved © 2026 | Privacy Policy | Sitemap
Link to: Security Alert: NYS DMV Email Scam Going Around Link to: Security Alert: NYS DMV Email Scam Going Around Security Alert: NYS DMV Email Scam Going AroundEmail Phishing Link to: Sometimes Low-Tech is the way to go Link to: Sometimes Low-Tech is the way to go woman with laptop in officeSometimes Low-Tech is the way to go
Scroll to top Scroll to top Scroll to top
XSolutions IT
This website uses cookies
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}